Authenticity, integrity and provenance assurance across the cyber stack: A systematic review of detection, watermarking, authentication and cryptographic mechanisms
Keywords:
Systematic review, PRISMA 2020, Integrity assurance, Provenance verification, Repackaging detectionAbstract
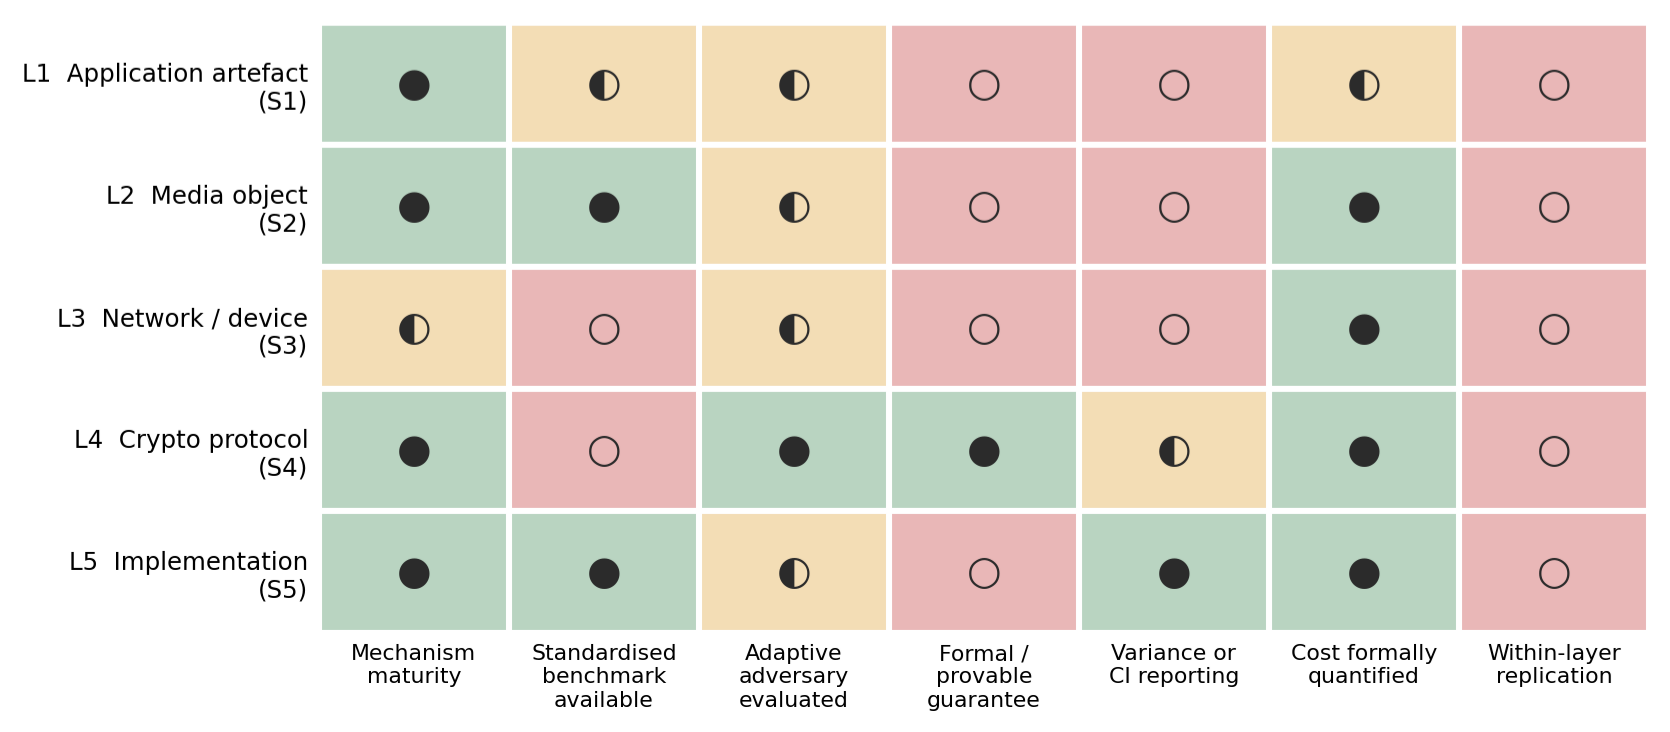
Assurance of authenticity, integrity and provenance recurs across the computing stack, but relevant research communities often publish in isolation. This protocol-driven systematic review appraises a bounded contemporary evidence base across five assurance layers--application, media, network, protocol and implementation--to identify cross-layer regularities and evidential asymmetries. Following PRISMA 2020, we enumerated peer-reviewed research published in Cyber Security and Applications, Volume 4 (2026), as available on 15 September 2026. Nine records were identified; four were excluded at title/abstract screening under the pre-specified eligibility criteria, and five satisfied all inclusion criteria at full-text assessment. Statistical heterogeneity precluded meta-analysis, so a narrative synthesis was undertaken. The included studies span application artefacts, media objects, physical-network devices, cryptographic protocols and micro-architectural implementations. Four use machine learning and one supplies security proofs with formal verification. Reported outcomes include watermark accuracy of 99.91%, spoofing-detection accuracy of 94.18%, total signcryption cost of 887 ms for ten receivers with linearly growing transmission cost, and recovery of a masked AES key within approximately 60 attack traces. Methodological quality ranged from 81.3% to 93.8%. Across layers, assurance mechanisms converge on an invariance principle: they seek representations stable under benign transformation but sensitive to adversarial modification. The evidence also shows an asymmetry between empirical and provable assurance and uneven benchmark maturity across layers. The review was not prospectively registered; the protocol is reproduced in Section 2 and Appendices A--C.
References
[1] Y. Wu, Z. Liu, Y. Lin, B. Zhao, C. Zhou, T. Wu & Z. Hong, ``Android app repackaging detection: a comprehensive survey'', Cyber Security and Applications 4 (2026) 100124. https://doi.org/10.1016/j.csa.2026.100124. DOI: https://doi.org/10.1016/j.csa.2026.100124
[2] S. Wen, H. Tan, J. Li & T. Hu, ``A robust audio watermarking method based on dual-encoder U-Net and short-time Fourier transform'', Cyber Security and Applications 4 (2026) 100129. https://doi.org/10.1016/j.csa.2026.100129. DOI: https://doi.org/10.1016/j.csa.2026.100129
[3] B. Achaal, M. Adda, M. Berger & A. Awde, ``An intelligent authentication and intrusion detection system for securing advanced metering infrastructure'', Cyber Security and Applications 4 (2026) 100115. https://doi.org/10.1016/j.csa.2025.100115. DOI: https://doi.org/10.1016/j.csa.2025.100115
[4] Y. Zhao, X. Liu, Y. Zhou, B. Yang & M. Zhang, ``A multi-receiver and multi-message anonymous ID-based hybrid signcryption scheme for secure data transmission'', Cyber Security and Applications 4 (2026) 100128. https://doi.org/10.1016/j.csa.2026.100128. DOI: https://doi.org/10.1016/j.csa.2026.100128
[5] A. Amrouche, L. Boubchir & S. Yahiaoui, ``Metaheuristic-driven neural architecture search for deep learning-based side-channel analysis'', Cyber Security and Applications 4 (2026) 100125. https://doi.org/10.1016/j.csa.2026.100125. DOI: https://doi.org/10.1016/j.csa.2026.100125
[6] M. J. Page, J. E. McKenzie, P. M. Bossuyt, I. Boutron, T. C. Hoffmann, C. D. Mulrow, L. Shamseer, J. M. Tetzlaff, E. A. Akl, S. E. Brennan, R. Chou, J. Glanville, J. M. Grimshaw, A. Hróbjartsson, M. M. Lalu, T. Li, E. W. Loder, E. Mayo-Wilson, S. McDonald, L. A. McGuinness, L. A. Stewart, J. Thomas, A. C. Tricco, V. A. Welch, P. Whiting & D. Moher, ``The PRISMA 2020 statement: an updated guideline for reporting systematic reviews'', BMJ 372 (2021) n71. https://doi.org/10.1136/bmj.n71. DOI: https://doi.org/10.1136/bmj.n71
[7] H. Li, Z. Yao, B. Wu, C. Gao, T. Xu, W. Yuan & X. Luo, ``Automated mass malware factory: the convergence of piggybacking and adversarial example in Android malicious software generation'', Proceedings of the 32nd Network and Distributed System Security Symposium (NDSS), San Diego, USA, 2025. https://doi.org/10.14722/ndss.2025.241933. DOI: https://doi.org/10.14722/ndss.2025.241933
[8] L. Li, T. F. Bissyandé & J. Klein, ``Rebooting research on detecting repackaged Android apps: literature review and benchmark'', IEEE Transactions on Software Engineering 47 (2021) 676. https://doi.org/10.1109/TSE.2019.2901679. DOI: https://doi.org/10.1109/TSE.2019.2901679
[9] X. Zhan, T. Zhang & Y. Tang, ``A comparative study of Android repackaged apps detection techniques'', 2019 IEEE 26th International Conference on Software Analysis, Evolution and Reengineering (SANER), Hangzhou, China, 2019, pp. 321--331. https://doi.org/10.1109/SANER.2019.8667975. DOI: https://doi.org/10.1109/SANER.2019.8667975
[10] W. Zhou, Y. Zhou, X. Jiang & P. Ning, ``Detecting repackaged smartphone applications in third-party Android marketplaces'', Proceedings of the Second ACM Conference on Data and Application Security and Privacy (CODASPY), San Antonio, USA, 2012, pp. 317--326. https://doi.org/10.1145/2133601.2133640. DOI: https://doi.org/10.1145/2133601.2133640
[11] K. Allix, T. F. Bissyandé, J. Klein & Y. Le Traon, ``AndroZoo: collecting millions of Android apps for the research community'', Proceedings of the 13th International Conference on Mining Software Repositories (MSR '16), Austin, USA, 2016, pp. 468--471. https://doi.org/10.1145/2901739.2903508. DOI: https://doi.org/10.1145/2901739.2903508
[12] T. S. John, T. Thomas & S. Emmanuel, ``Detection of evasive Android malware using EigenGCN'', Journal of Information Security and Applications 86 (2024) 103880. https://doi.org/10.1016/j.jisa.2024.103880. DOI: https://doi.org/10.1016/j.jisa.2024.103880
[13] L. Zhan, J. Ming, J. Fu, G. Peng, L. Sha & L. Lan, ``The hidden complexities of Android TPL detection: an empirical analysis of techniques, challenges, and effectiveness'', Computers & Security 159 (2025) 104672. https://doi.org/10.1016/j.cose.2025.104672. DOI: https://doi.org/10.1016/j.cose.2025.104672
[14] Z. Zhang, S. Luo, Y. Lu & L. Pan, ``Obfuscation-resilient detection of Android third-party libraries using multi-scale code dependency fusion'', Information Fusion 117 (2025) 102908. https://doi.org/10.1016/j.inffus.2024.102908. DOI: https://doi.org/10.1016/j.inffus.2024.102908
[15] Q. Zeng, L. Luo, Z. Qian, X. Du & Z. Li, ``Resilient decentralized Android application repackaging detection using logic bombs'', Proceedings of the 2018 International Symposium on Code Generation and Optimization (CGO), Vienna, Austria, 2018, pp. 50--61. https://doi.org/10.1145/3168820. DOI: https://doi.org/10.1145/3168820
[16] G. Lin, W. Luo, P. Zheng & J. Huang, ``An audio watermarking method against re-recording distortions'', Pattern Recognition 162 (2025) 111366. https://doi.org/10.1016/j.patcog.2025.111366. DOI: https://doi.org/10.1016/j.patcog.2025.111366
[17] C. Liu, J. Zhang, H. Fang, Z. Ma, W. Zhang & N. Yu, ``DeAR: a deep-learning-based audio re-recording resilient watermarking'', Proceedings of the AAAI Conference on Artificial Intelligence 37 (2023) 13201. https://doi.org/10.1609/aaai.v37i11.26550. DOI: https://doi.org/10.1609/aaai.v37i11.26550
[18] C. Liu, J. Zhang, T. Zhang, X. Yang, W. Zhang & N. Yu, ``Detecting voice cloning attacks via timbre watermarking'', arXiv preprint arXiv:2312.03410 (2023). Available online: https://arxiv.org/abs/2312.03410. DOI: https://doi.org/10.14722/ndss.2024.24200
[19] G. Hua, J. Huang, Y. Q. Shi, J. Goh & V. L. L. Thing, ``Twenty years of digital audio watermarking: a comprehensive review'', Signal Processing 128 (2016) 222. https://doi.org/10.1016/j.sigpro.2016.04.005. DOI: https://doi.org/10.1016/j.sigpro.2016.04.005
[20] F. T. Liu, K. M. Ting & Z.-H. Zhou, ``Isolation Forest'', Proceedings of the IEEE International Conference on Data Mining (ICDM), Pisa, Italy, 2008, pp. 413--422. https://doi.org/10.1109/ICDM.2008.17. DOI: https://doi.org/10.1109/ICDM.2008.17
[21] A. Pourghasem, R. Kirner, A. Tsokanos, I. Mporas & A. Mylonas, ``Machine learning and deep learning-based multi-attribute physical-layer authentication for spoofing detection in LoRaWAN'', Future Internet 17 (2025) 68. https://doi.org/10.3390/fi17020068. DOI: https://doi.org/10.3390/fi17020068
[22] Z. Yun & M. F. Iskander, ``Ray tracing for radio propagation modeling: principles and applications'', IEEE Access 3 (2015) 1089. https://doi.org/10.1109/ACCESS.2015.2453991. DOI: https://doi.org/10.1109/ACCESS.2015.2453991
[23] B. Achaal, M. Adda, M. Berger, H. Ibrahim & A. Awde, ``Study of smart grid cybersecurity: examining architectures, communication networks, cyber-attacks, countermeasure techniques and challenges'', Cybersecurity 7 (2024) 10. https://doi.org/10.1186/s42400-023-00200-w. DOI: https://doi.org/10.1186/s42400-023-00200-w
[24] Y. Zheng, ``Digital signcryption or how to achieve cost(signature and encryption) $leq$ cost(signature) + cost(encryption)'', in Advances in Cryptology -- CRYPTO '97, B. S. Kaliski (Ed.), Springer, Berlin, Germany, 1997, pp. 165--179. https://doi.org/10.1007/BFb0052234. DOI: https://doi.org/10.1007/BFb0052234
[25] R. Cramer & V. Shoup, ``Design and analysis of practical public-key encryption schemes secure against adaptive chosen ciphertext attack'', SIAM Journal on Computing 33 (2003) 167. https://doi.org/10.1137/S0097539702403773. DOI: https://doi.org/10.1137/S0097539702403773
[26] A. W. Dent, ``Hybrid signcryption schemes with outsider security'', in Information Security -- ISC 2005, J. Zhou, J. Lopez, R. H. Deng & F. Bao (Eds.), Springer, Berlin, Germany, 2005, pp. 203--217. https://doi.org/10.1007/11556992_15. DOI: https://doi.org/10.1007/11556992_15
[27] Y. Zhou, R. Xu, Z. Qiao, B. Yang, Z. Xia & M. Zhang, ``An anonymous and efficient multimessage and multireceiver certificateless signcryption scheme for VANET'', IEEE Internet of Things Journal 10 (2023) 22823. https://doi.org/10.1109/JIOT.2023.3305489. DOI: https://doi.org/10.1109/JIOT.2023.3305489
[28] Y. Liang, H. Yan & Y. Liu, ``Unlinkable signcryption scheme for multi-receiver in VANETs'', IEEE Transactions on Intelligent Transportation Systems 24 (2023) 10138. https://doi.org/10.1109/TITS.2023.3271110. DOI: https://doi.org/10.1109/TITS.2023.3271110
[29] L. Wu, G. Perin & S. Picek, ``I choose you: automated hyperparameter tuning for deep learning-based side-channel analysis'', IEEE Transactions on Emerging Topics in Computing 12 (2024) 546. https://doi.org/10.1109/TETC.2022.3218372. DOI: https://doi.org/10.1109/TETC.2022.3218372
[30] S. Picek, G. Perin, L. Mariot, L. Wu & L. Batina, ``SoK: deep learning-based physical side-channel analysis'', ACM Computing Surveys 55 (2023) 227:1. https://doi.org/10.1145/3569577. DOI: https://doi.org/10.1145/3569577
[31] H. Maghrebi, T. Portigliatti & E. Prouff, ``Breaking cryptographic implementations using deep learning techniques'', in Security, Privacy and Applied Cryptography Engineering (SPACE 2016), C. Carlet, M. A. Hasan & V. Saraswat (Eds.), Springer, Cham, Switzerland, 2016, pp. 3--26. https://doi.org/10.1007/978-3-319-49445-6_1. DOI: https://doi.org/10.1007/978-3-319-49445-6_1
[32] P. Kocher, J. Jaffe & B. Jun, ``Differential power analysis'', in Advances in Cryptology -- CRYPTO '99, M. Wiener (Ed.), Springer, Berlin, Germany, 1999, pp. 388--397. https://doi.org/10.1007/3-540-48405-1_25. DOI: https://doi.org/10.1007/3-540-48405-1_25
[33] S. Chari, J. R. Rao & P. Rohatgi, ``Template attacks'', in Cryptographic Hardware and Embedded Systems -- CHES 2002, B. S. Kaliski, Ç. K. Koç & C. Paar (Eds.), Springer, Berlin, Germany, 2003, pp. 13--28. https://doi.org/10.1007/3-540-36400-5_3. DOI: https://doi.org/10.1007/3-540-36400-5_3
[34] T. Elsken, J. H. Metzen & F. Hutter, ``Neural architecture search: a survey'', Journal of Machine Learning Research 20 (2019) 1. Available online: https://www.jmlr.org/papers/v20/18-598.html.
[35] A. Gohr, S. Jacob & W. Schindler, ``CHES 2018 side channel contest CTF: solution of the AES challenges'', Cryptology ePrint Archive, Report 2019/094, 2019. Available online: https://eprint.iacr.org/2019/094.
[36] N. Gupta, A. Jati & A. Chattopadhyay, ``AI attacks AI: recovering neural network architecture from NVDLA using AI-assisted side-channel attack'', ACM Transactions on Embedded Computing Systems 24 (2025) 75. https://doi.org/10.1145/3731560. DOI: https://doi.org/10.1145/3731560
[37] M. Defferrard, K. Benzi, P. Vandergheynst & X. Bresson, ``FMA: a dataset for music analysis'', arXiv preprint arXiv:1612.01840 (2016). Available online: https://arxiv.org/abs/1612.01840.
[38] V. Panayotov, G. Chen, D. Povey & S. Khudanpur, ``LibriSpeech: an ASR corpus based on public-domain audio books'', 2015 IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP), Brisbane, Australia, 2015, pp. 5206--5210. https://doi.org/10.1109/ICASSP.2015.7178964. DOI: https://doi.org/10.1109/ICASSP.2015.7178964
[39] P. Tian, F. Yang, X. Ma, C. A. Boano, X. Tian, Y. Liu & J. Wei, ``Dataset: environmental impact on the long-term connectivity and link quality of an outdoor LoRa network'', Proceedings of the 19th ACM Conference on Embedded Networked Sensor Systems (SenSys), Coimbra, Portugal, 2021, pp. 565--568. https://doi.org/10.1145/3485730.3493696. DOI: https://doi.org/10.1145/3485730.3493696
[40] F. Pierazzi, F. Pendlebury, J. Cortellazzi & L. Cavallaro, ``Intriguing properties of adversarial machine-learning attacks in the problem space'', 2020 IEEE Symposium on Security and Privacy (S&P), San Francisco, USA, 2020, pp. 1332--1349. https://doi.org/10.1109/SP40000.2020.00073. DOI: https://doi.org/10.1109/SP40000.2020.00073
Published
How to Cite
Issue
Section
Copyright (c) 2026 Kolawole Olamide Michael, Lebo Norabel Ikaka, Nathaniel Etim Effiom, Murphy Reje-Okim Mbeh, Faith Bassey-Ita Bassey, Bitrus Levi Garki, Oyui Daniel Lawrence, Samuel Okon Essang

This work is licensed under a Creative Commons Attribution 4.0 International License.